Enter URL
Enter the website URL whose cookies you want to audit (e.g. https://example.com).
Audit Set-Cookie flags: Secure, HttpOnly and SameSite on every cookieCookies carry session tokens, the keys to logged-in accounts, and a single missing flag can let an attacker steal one. Enter a URL to see every cookie your site sets with its security flags laid bare.
Audit Set-Cookie flags: Secure, HttpOnly and SameSite on every cookie
Enter the website URL whose cookies you want to audit (e.g. https://example.com).
Click "Check Cookies" and wait while the Set-Cookie headers are fetched.
Review each cookie flag verdict and apply the recommended fixes.
Cookies carry the keys to user sessions, yet their security flags are set once and forgotten. The Cookie Security Checker reads every Set-Cookie header your server sends and audits each flag individually.
Each cookie gets its own verdict with plain-language explanations, so you can see exactly which flag to add where.
The moments exposed cookies get found.
Run it before launch as part of a pre-release security review, when fixes are cheapest.
Re-check after any change to login, sessions, or third-party integrations, since new cookies creep in silently.
Demonstrate that session management follows basic hardening practice with an evidence-backed report.
Know exactly which cookies your site depends on as browsers phase third-party cookies out.
The findings that matter most.
Session cookies sent over unencrypted connections can be stolen; Secure restricts them to HTTPS only.
Without it, any injected JavaScript can read the cookie through document.cookie and steal the session.
Lax blocks most cross-site request forgery; None is only for cookies that must travel cross-site, with Secure alongside.
It takes seconds and needs no signup, and often surfaces the low-effort, high-impact fix that makes a security audit worthwhile.
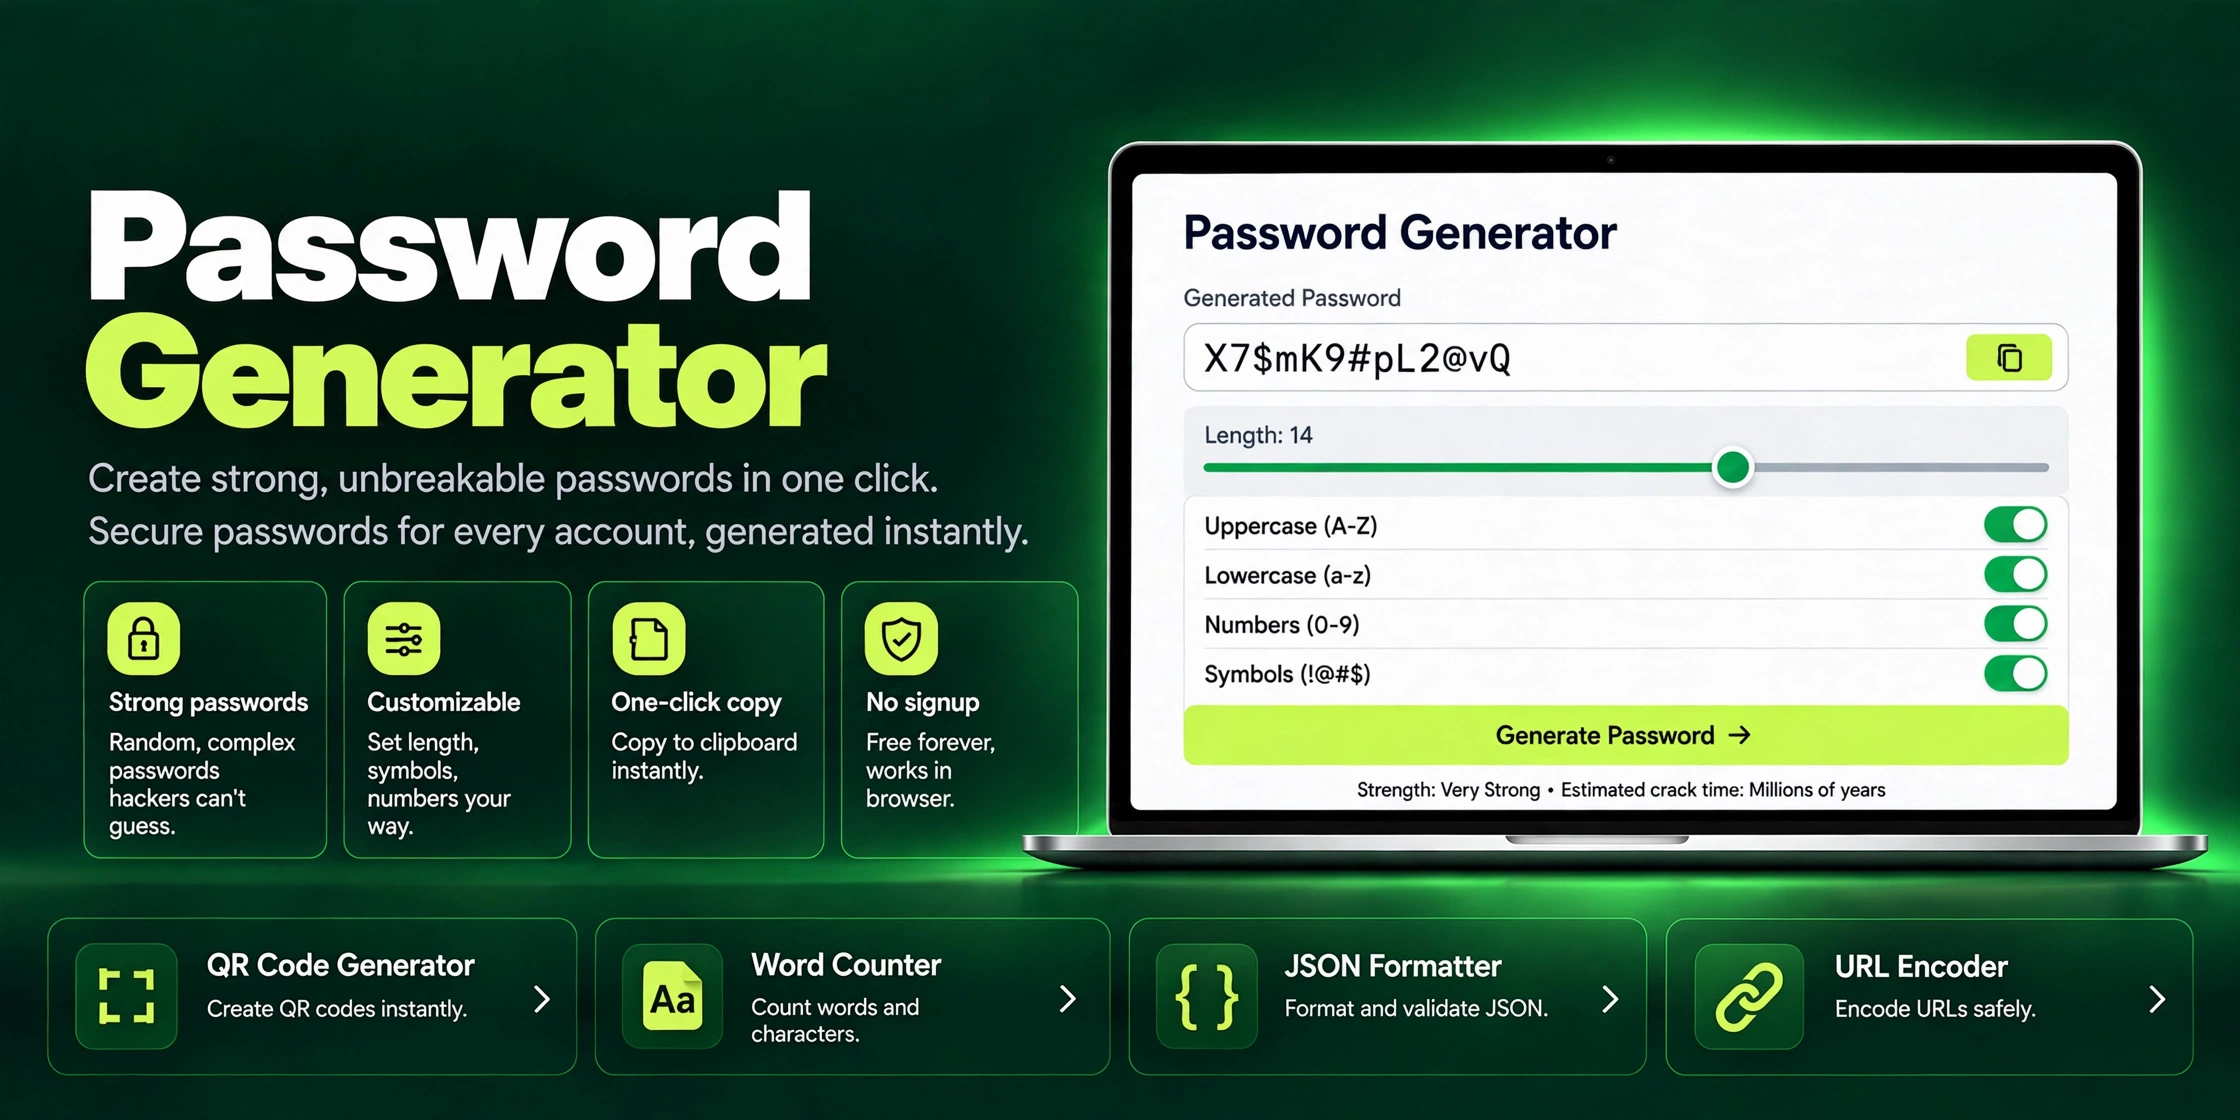
Generate strong, unbreakable passwords in one click with ZaxisMedia's free Password Generator. Customizable length, symbols & one-click copy. No signup needed.
Read article →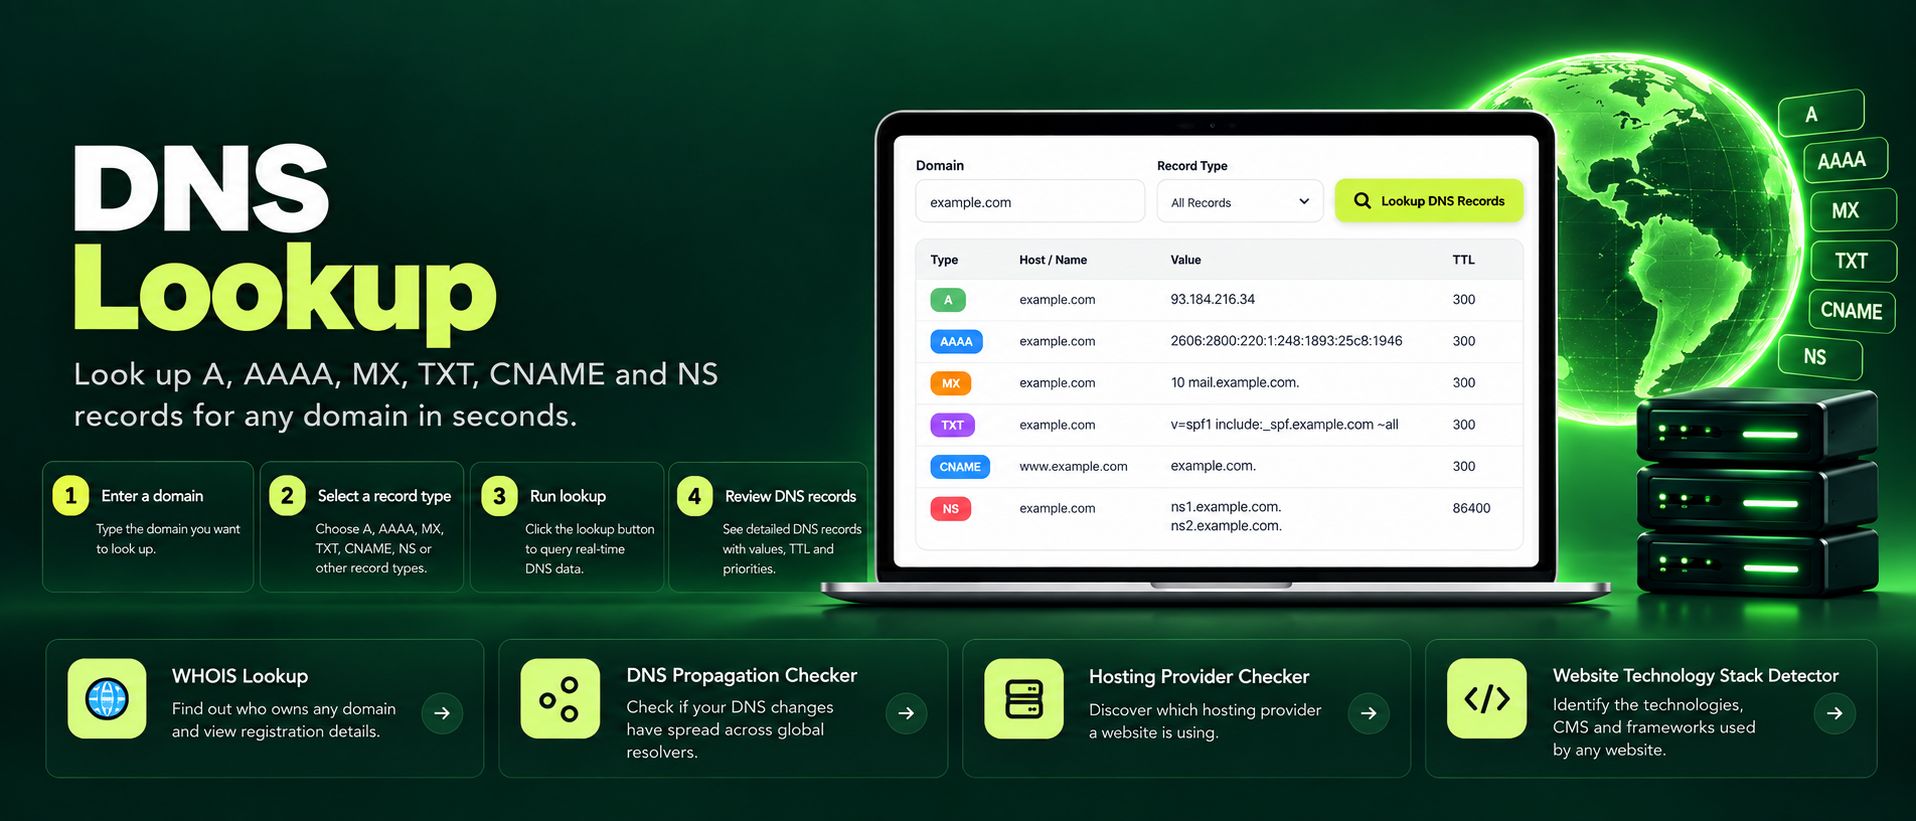
Free online DNS lookup tool. Check A, AAAA, MX, TXT, CNAME, NS and SOA records for any domain instantly. Fast, private, accurate, no sign-up required.
Read article →