Enter domain
Enter the domain you want to check (e.g. example.com).
Check if a domain is signed with DNSSEC and validate the chainDNS answers can be forged on the path between your resolver and the nameserver. DNSSEC is the cryptographic answer, and this checker validates whether a domain's DNSSEC chain actually holds together.
Check if a domain is signed with DNSSEC and validate the chain
Enter the domain you want to check (e.g. example.com).
Click "Check DNSSEC" to query the live DNSKEY and DS records.
Review the signed status, key algorithms, key tags, and chain of trust.
Standard DNS has no authentication, so an attacker can forge answers and redirect visitors. DNSSEC fixes this by signing every record set, and this checker confirms the protection is in place. It reports key algorithms and KSK/ZSK roles, and flags the common misconfiguration: a signed zone with no DS record at the parent.
Where a broken chain hurts.
Enabling DNSSEC at the registrar and provider is only half the job; this catches chains broken by key rollovers.
Banking, email infrastructure and government sites belong in the audit routine for any domain that matters.
A missing DS record at the registrar is one of the most common ways the chain breaks silently.
When DNSSEC breaks, legitimate resolution can fail too, not just spoofed answers getting through to users.
How the validation works.
The checker walks the delegation from the parent zone and confirms the DS record exists where it should.
It retrieves the DNSKEY records holding the zone's public keys so signatures can be verified.
Record signatures are checked against the keys, with the failing link identified: missing DS, broken rollover, or invalid signatures.
A clear pass or fail with the failing link identified, from public DNS data. No signup needed.
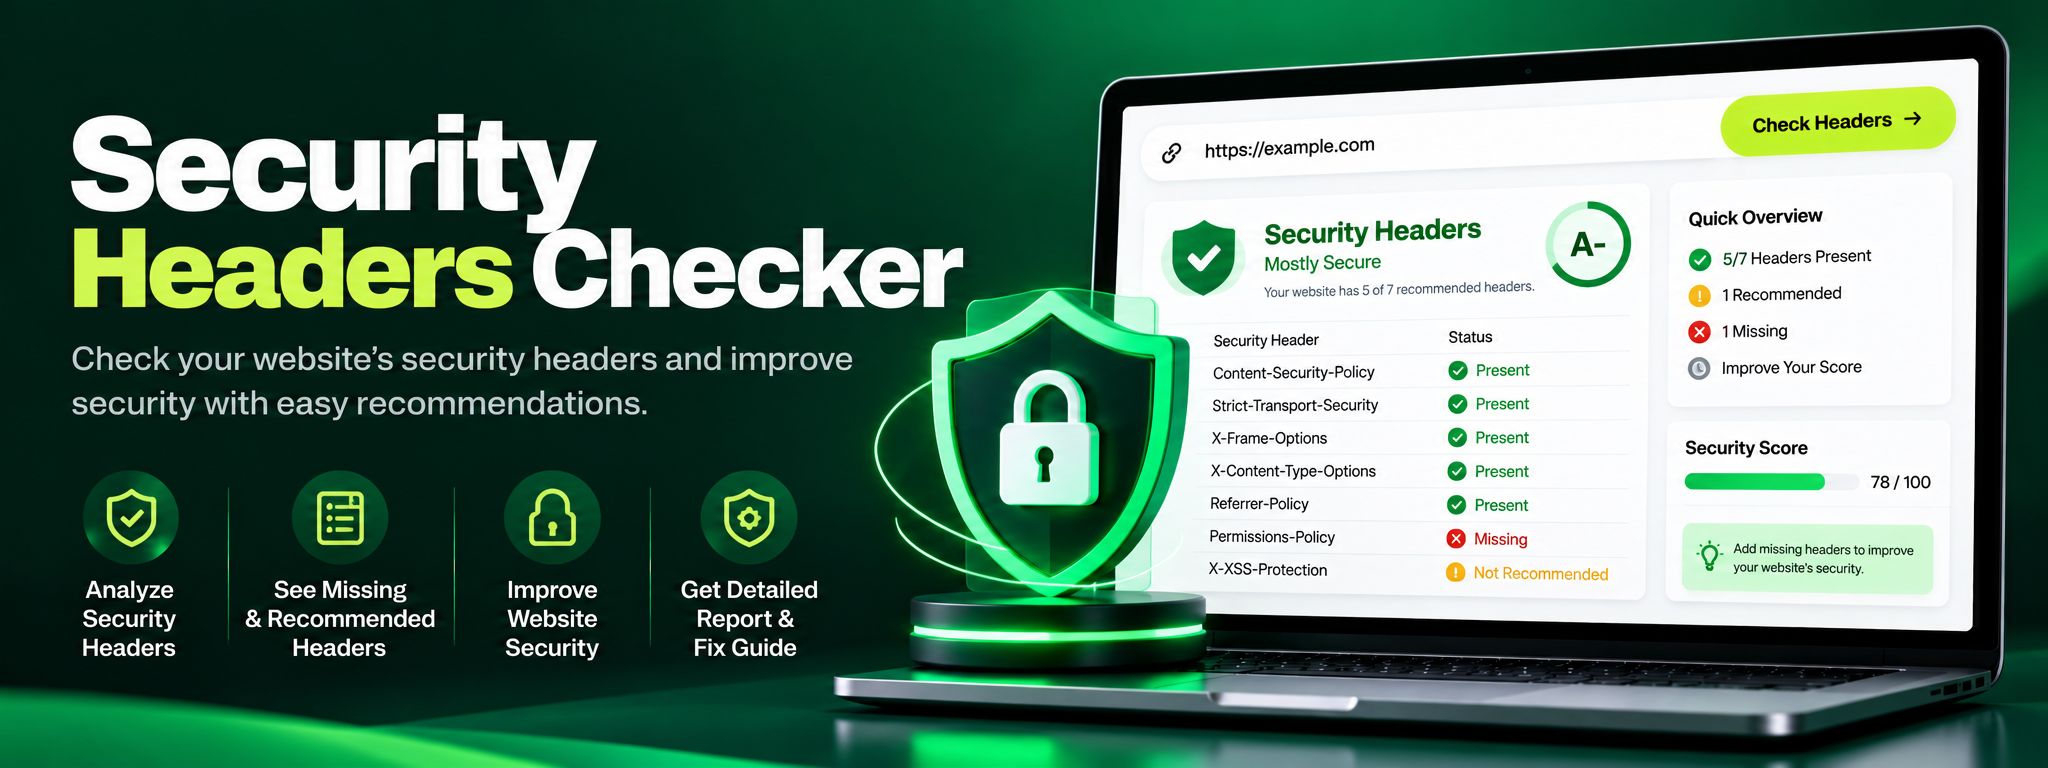
Free security headers checker. Instantly scan HSTS, CSP, X-Frame-Options and more on any site, get an A to F grade and clear steps to fix every website gap.
Read article →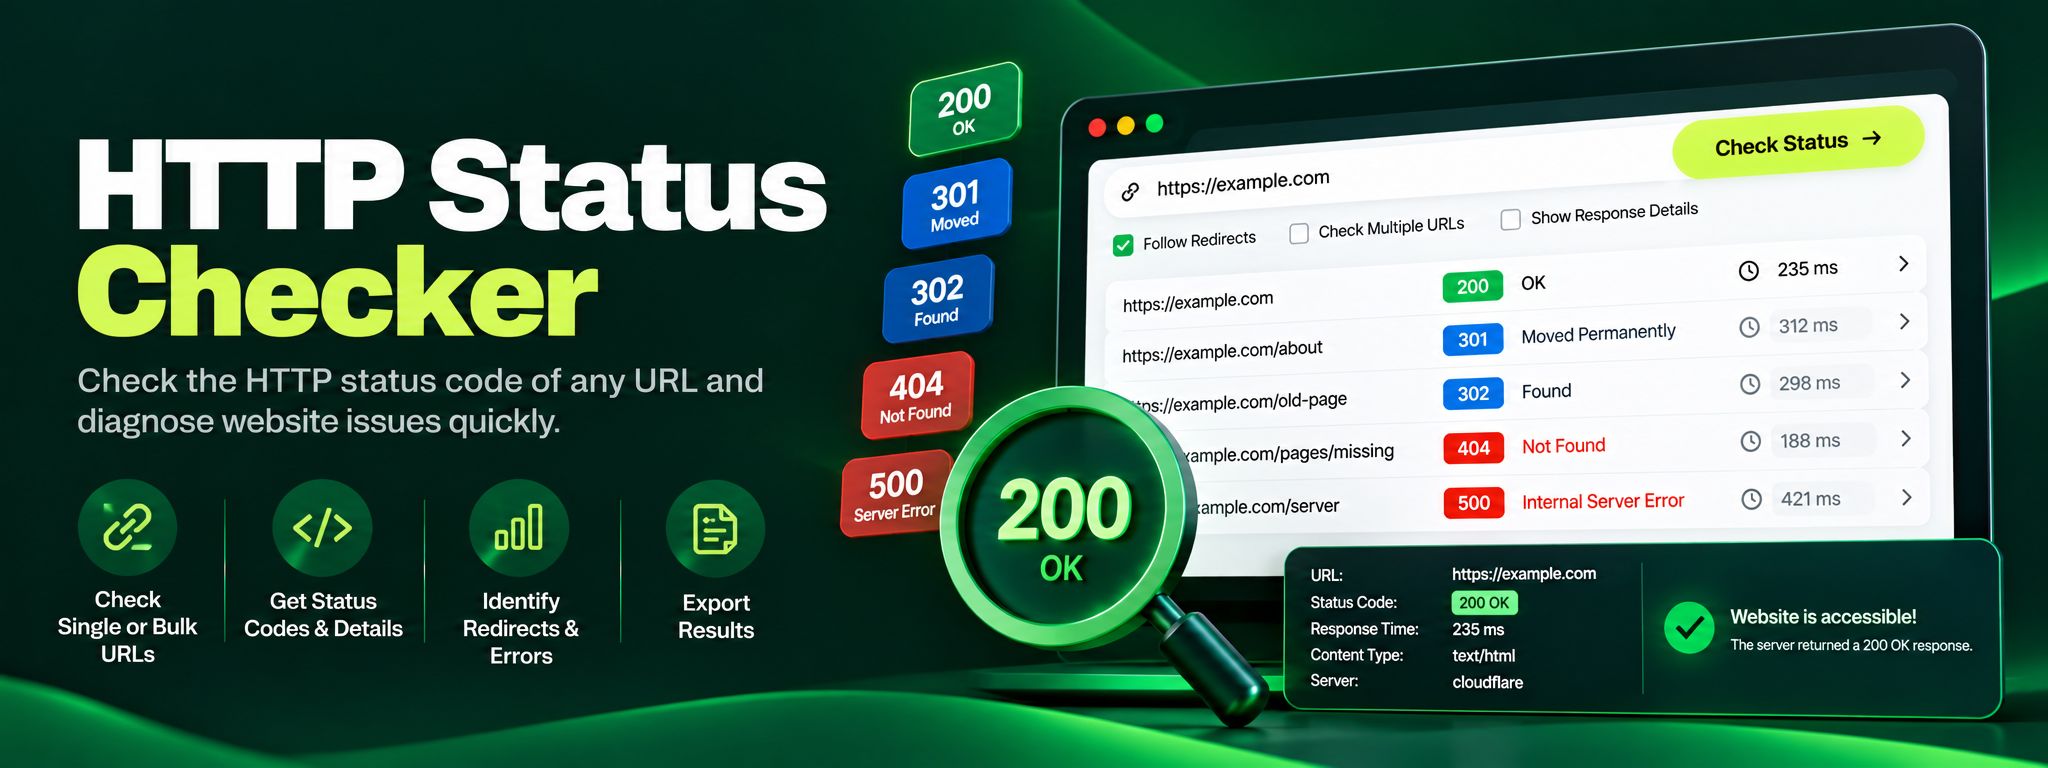
Free HTTP status checker. Check any URL's status code, trace redirect chains hop by hop, and fix 404, 301 and 500 errors before they silently hurt your SEO.
Read article →