Enter URL
Enter the resource URL to test (e.g. https://example.com/api/data).
Send a real preflight and see exactly who can read your resources cross-originYour app works on localhost, then every API call fails in production: nine times out of ten it is a CORS misconfiguration. Paste any URL and see exactly what the server is declaring, header by header.
Send a real preflight and see exactly who can read your resources cross-origin
Enter the resource URL to test (e.g. https://example.com/api/data).
Optionally set the Origin to test from, then click "Check CORS Headers".
Review the preflight result, the verdict, and any misconfigurations.
CORS errors are among the most confusing failures in web development: the request works in curl and fails in the browser. The CORS Headers Checker reproduces the browser's preflight handshake and reads back every Access-Control header.
Each finding is explained in plain language, distinguishing wide-open access from properly restricted origins, so the fix is obvious.
The moments CORS blocks real work.
See the exact header values behind a blocked request instead of guessing at the configuration.
Verify the right origins are exposed on staging and production before a partner integration ships.
Hunt for policies that hand out access too freely and tighten them before attackers notice.
Catch missing preflight responses that break PUT, DELETE, and JSON requests.
What the findings actually mean.
Browsers reject Access-Control-Allow-Origin: * combined with credentials outright; the server must echo the specific origin.
Without Access-Control-Max-Age, browsers re-run the OPTIONS check on every complex request, adding needless latency.
This header stops caches from serving one origin's CORS response to another, a subtle bug the report covers.
Findings come back in plain language you can hand straight to whoever owns the server configuration. No signup, results in seconds.
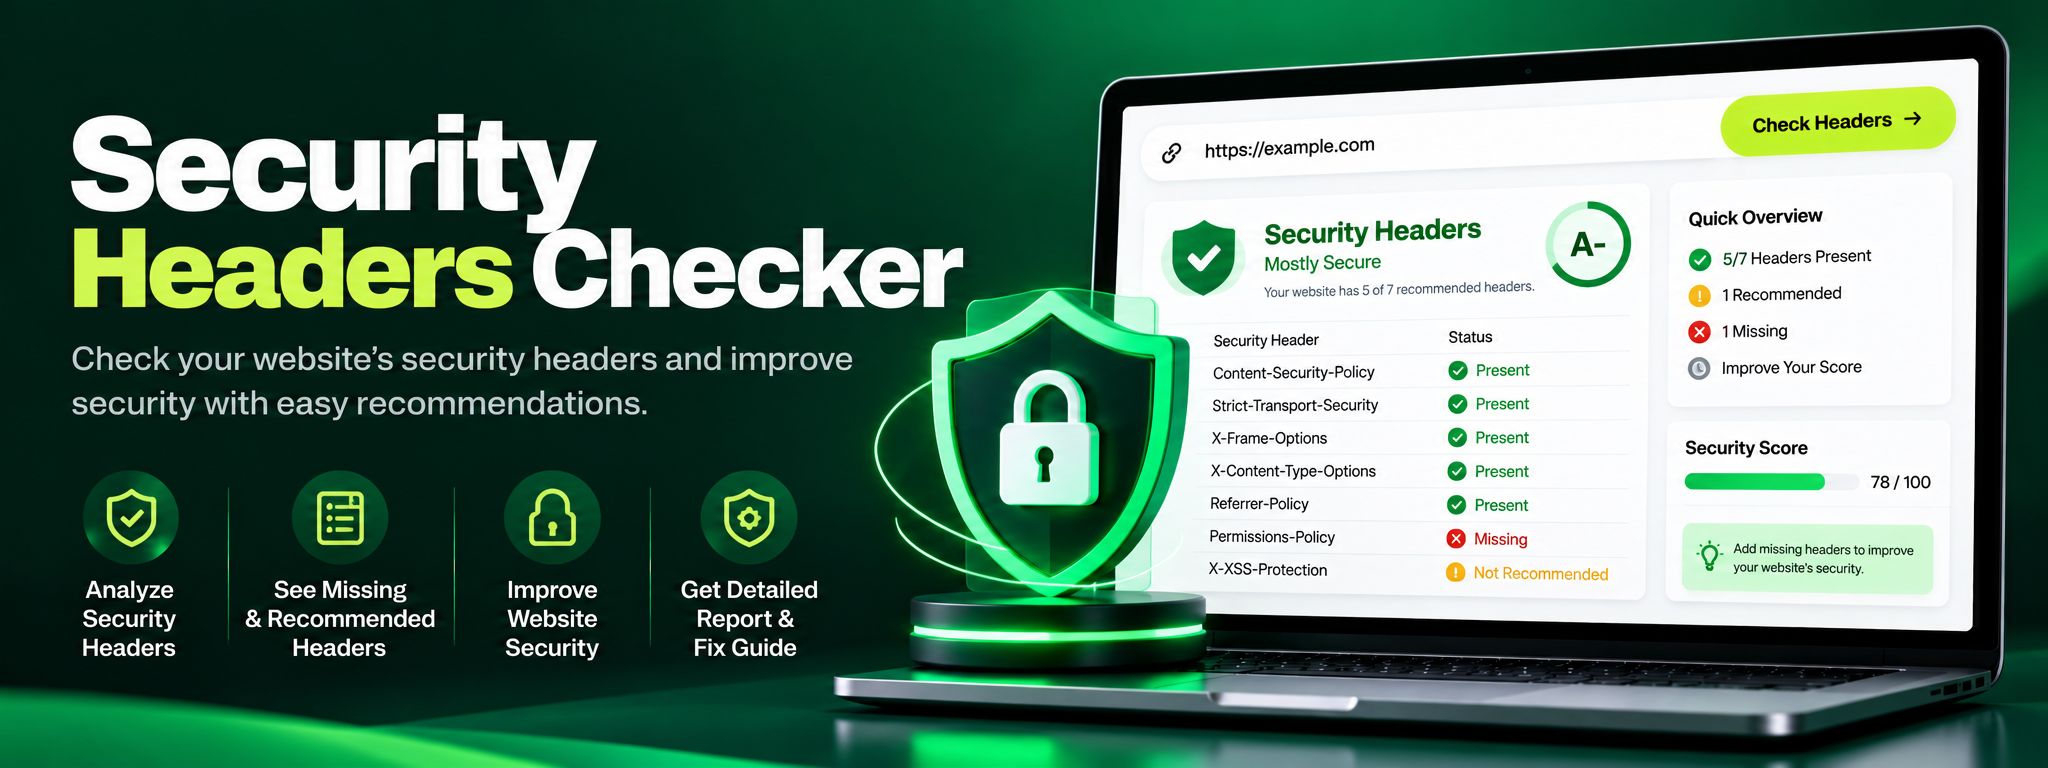
Free security headers checker. Instantly scan HSTS, CSP, X-Frame-Options and more on any site, get an A to F grade and clear steps to fix every website gap.
Read article →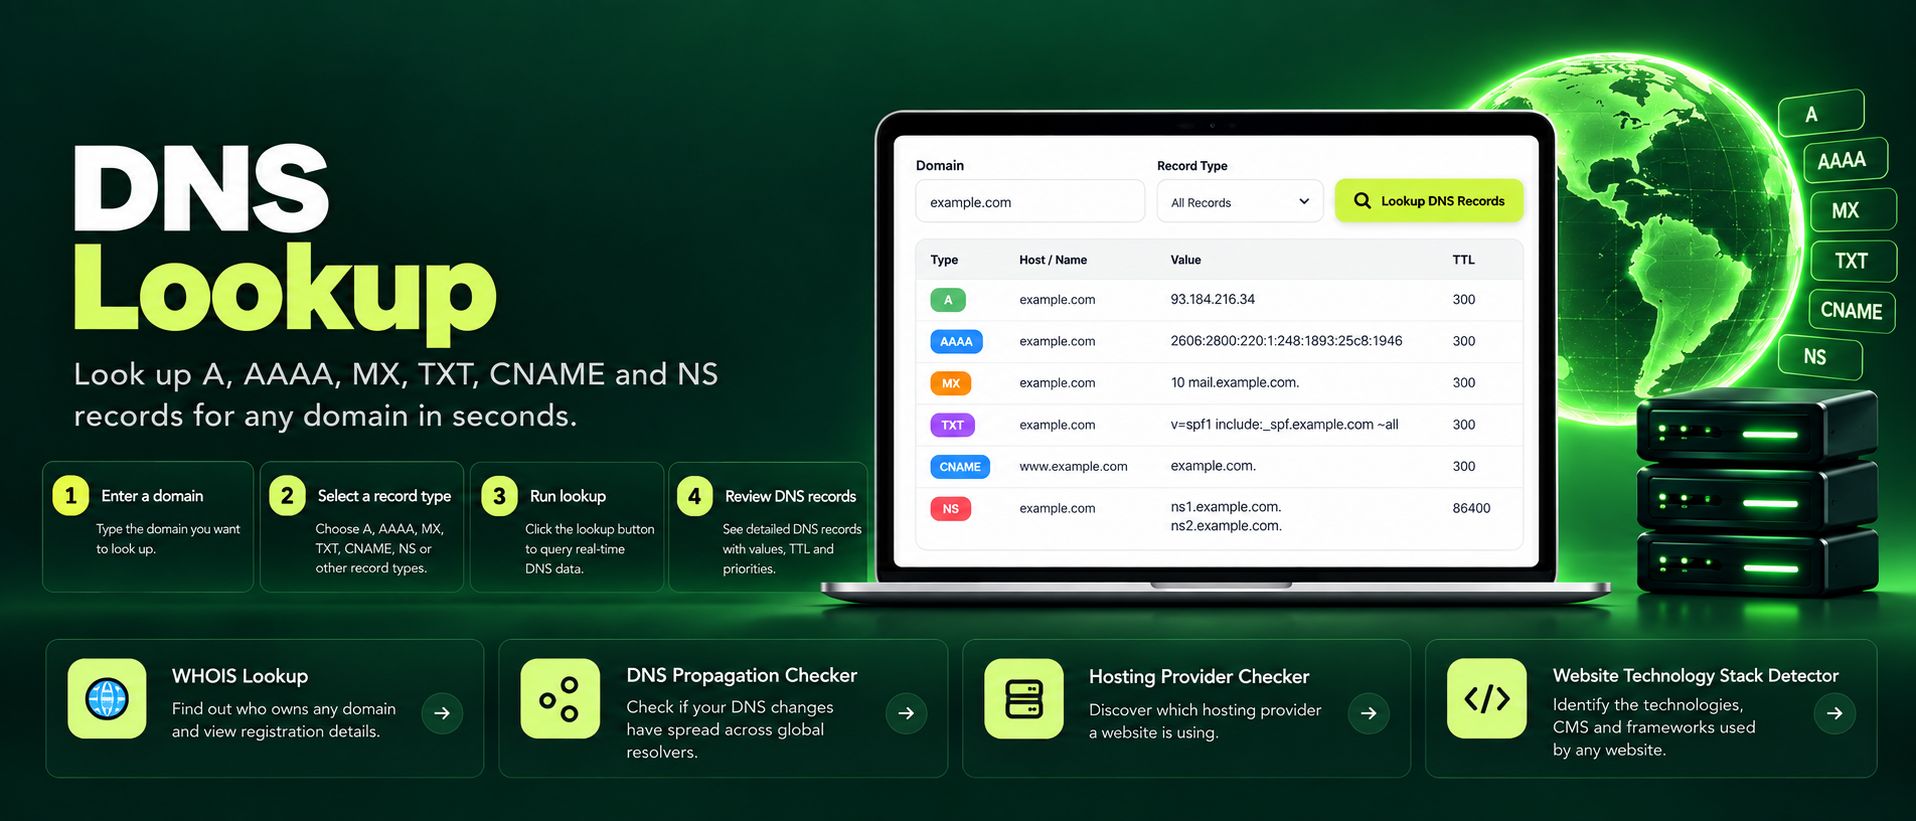
Free online DNS lookup tool. Check A, AAAA, MX, TXT, CNAME, NS and SOA records for any domain instantly. Fast, private, accurate, no sign-up required.
Read article →